
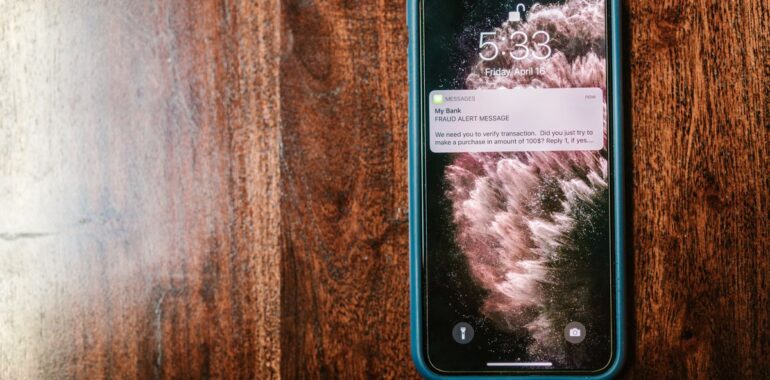
Fake toll fine scam: decoding the industrial phishing Microsoft just disrupted
A text tells you about an unpaid $6.85 toll and threatens to suspend your registration tonight. This fake toll fine scam isn’t the work of a lone fraudster: on October 14, 2026, Microsoft announced the disruption of YAM Store, an underground marketplace selling turnkey phishing kits (CoGUI, Haozi and Iron Man). Since January, this ecosystem enabled more than one billion emails and text messages sent to more than 75,000 organizations.
Here’s the lure taken apart, a checklist to hand to your employees and a quick self-assessment for your SMB.
What Microsoft disrupted
| Element | In short |
|---|---|
| YAM Store (Storm-3119) | Underground shop reselling hijacked or fraudulently created Microsoft 365 and Google environments, plus hosting for phishing pages |
| CoGUI, Haozi, Iron Man (Storm-2990) | Turnkey phishing kits; Iron Man has more than 2,300 templates impersonating governments, toll authorities, police, banks, postal services and retailers |
| Volume since January 2026 | More than 1 billion emails and text messages, to more than 75,000 organizations |
| Evasion techniques | Geofencing, fake CAPTCHAs, IP block lists and real-time Telegram alerts for the operator |
| Disruption (Oct. 14, 2026) | Domains seized under a U.S. federal court order, more than 20,000 accounts disabled and more than 100,000 domains blocked |
The fake toll fine scam, annotated
Fictional example based on the templates Microsoft describes. The badges match the legend.
Legend: the 6 clues of a fake toll fine scam
- 1An impersonated authority: government, police, tolls, postal service. Kits sold on YAM Store offer thousands of ready-made “official” templates.
- 2A tiny amount: $6.85, “not worth checking”. The real target is your card number.
- 3A very short deadline: urgency is the #1 red flag Microsoft saw in nearly every case.
- 4A disproportionate threat: fine, licence, legal action. No agency suspends a registration by text message.
- 5A domain that’s anything but official: unusual extension (.top), with “peage” and “qc” glued together to look real.
- 6“Reply Y”: a trick to make your phone treat the sender as known and activate the link.
⚠️ And after the click?
The page mimics an official payment portal and asks for the plate, then the credit card, then the code received by text. According to Microsoft, the operator receives every entry live on Telegram and can decide what the victim sees next. Some campaigns also abuse device code authentication to steal access to cloud accounts.
In other words: an employee who “only pays $6.85” can hand over their card and their Microsoft 365 account in under two minutes.
The checklist for your employees
✅ Fake fine, fake parcel, fake toll: the right reflexes
- ☐ I never pay a fine, a toll or a parcel fee from a link received by text or email. I type the official address myself or open the app.
- ☐ Small amount + very short deadline = I stop and check.
- ☐ I don’t reply “Y”, “O” or “STOP” to an unknown number.
- ☐ I never share a code received by text, and I never approve a sign-in request I didn’t start myself.
- ☐ If the notice is about a company vehicle, I forward it to the person in charge without paying.
- ☐ I report the message (“Report” button in Outlook; forward to 7726 for a text), then delete it.
- ☐ Clicked or entered information? I call IT support and my bank right away. No shame: speed matters most.
Self-assessment: can your SMB withstand industrial phishing?
5 or 6 points: solid base, stay the course. 3 or 4: two or three settings will close the biggest doors. 0 to 2: one well-crafted fake toll fine scam could be enough to open your Microsoft 365 environment.
This disruption slows fraudsters down but doesn’t stop them: other kits will take over. Also read our article on Microsoft 365 device code phishing, a technique seen in some of these campaigns, and on adversary-in-the-middle phishing targeting Microsoft 365. Proactive monitoring of your systems helps spot an unusual sign-in after a click. See our cybersecurity services, our cyber monitoring and our Microsoft 365 services.
Book your free cyber check
MFA, admin accounts, link filtering: our free cyber check verifies whether a fake toll fine scam could open your Microsoft 365 environment, and gives you a clear, jargon-free plan.
Call us at 438-476-2322 or email info@neotechcloudsolutions.com.
Sources
- Microsoft Threat Intelligence — The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime (October 14, 2026)
- Microsoft On the Issues — Disrupting the service economy behind transnational cybercrime operations (October 14, 2026)
- CSO Online — As phishing-as-a-service goes industrial, Microsoft takes down a marketplace behind 1 billion messages
Photo: RDNE Stock project, Pexels (Pexels licence).